Enterprise
Controls your auditors can verify. Not policies in a handbook.
For operators running branches across states — and for brands that want real visibility into their pest-control vendors. Built on isolation the database itself enforces, separation of duties in the software, and records no one can quietly rewrite.
Isolation the database enforces
Tenant separation via PostgreSQL Row-Level Security, forced on every table. The application role cannot bypass it. Proven by tests in both directions.
Separation of duties, in the software
No one approves their own contract — not the author, not the owner. Overrides are audited with notes that can never be cleared.
Records that can't be rewritten
Invoices freeze at issue. Contract history is append-only with time travel. Stock is an immutable ledger. Where an auditor asks 'prove it', the data model is the proof.
Data isolation
Your data, isolated by the database itself.
Most SaaS vendors filter your data in application code and ask you to trust the filter. VectorAxe makes a stronger claim: the database enforces the walls, the application cannot bypass them, and automated tests prove it in both directions.
- Row-Level Security enabled and forced on every business table
- The tenant ID is written by the database — it cannot be forged from application code
- Fail-closed everywhere: no tenant context means zero rows, not all rows
Multi-branch
Six branches, one truth.
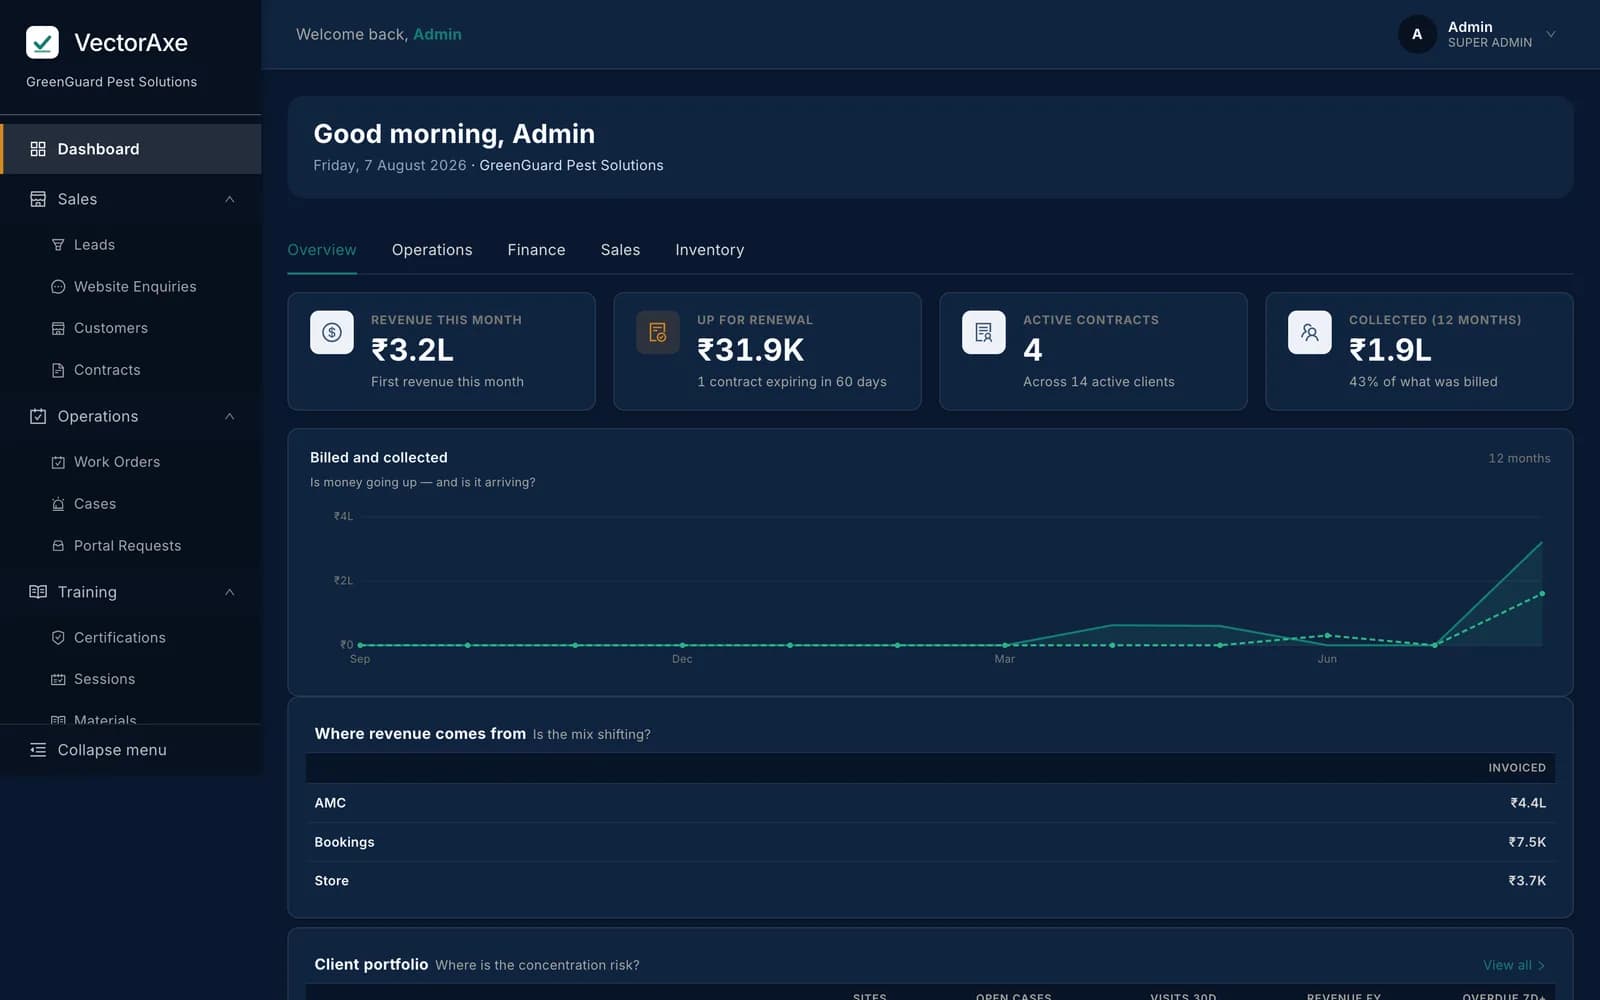
Multi-branch isn't a filter on a list. It's built into dispatch, invoicing, stock, and reporting — with an executive view over all of it.
Branch-matched dispatch
Work orders dispatch within the site's assigned branch. Only owners can override — and every override is flagged and recorded.
Branch-correct money
Each branch carries its own GSTIN and banking details. Invoices take their tax identity from the branch that serves the site — correct across states, automatically.
Per-branch stock and reporting
Stock levels, transfers, and low-stock alerts per branch; reports that slice by branch, so you see which operation carries which numbers.
Bulk onboarding
Migrate a multi-branch book in hours: spreadsheet imports for customers, sites, contacts, branches, and staff — every row previewed and classified before anything commits.
Roles & permissions
Access control that fits your org chart.
Role-based access designed for how field-service companies actually delegate — and documented by the system itself.
- Six system roles out of the box — from owner to field technician to finance
- ~85 named permissions across 77 enforced rules and 11 permission tiers — and growing every release
- Custom roles: start from a system role, grant or revoke individual permissions — an 'Auditor' or 'Store Supervisor' seat takes minutes
- Field-level commercial redaction: costs, bank details, and PAN hidden from non-commercial seats
- A read-only permissions matrix generated from the same data structure that enforces access — documentation cannot drift from enforcement
Security posture
The rest of the security story.
Four separate identity planes
Staff, client portal, platform console, and anonymous public are structurally separate authentication walls, each with its own token audience. A portal token is useless against the staff system — and tests prove it.
Backups and recovery
Daily automated backups with 14 retained, plus 7-day point-in-time recovery. Payment credentials AES-256-GCM encrypted at rest; secrets in a managed vault; HTTPS everywhere.
Changes take effect immediately
Suspension, access, and permission changes apply on the very next request — live sessions included. No waiting for the next login.
~1,700 automated tests — and growing every release
Run against a real PostgreSQL database on every change, including deployment-shaped tests that assert row-level security is forced on every table. The permission model is machine-verified between frontend and backend.
Security, this quarter.
Security work never stops. This is what's shipping next — told to you the same way we tell you our limits.
Comprehensive audit log
Every change to every record — who, what, when, and from where — queryable per tenant.
Login protection
Rate limiting and brute-force lockout on all authentication planes.
Session control
See every active session on your account, and revoke any of them in one click.
Multi-factor authentication
A second factor for staff accounts, enforced per tenant.
Password policy enforcement
Tenant-defined minimums for length, complexity, and rotation.
Bring your security questionnaire to the demo — we answer it line by line, including what's on the roadmap.
Tailored to your operation
Configured for how you actually work.
VectorAxe isn't one-size-fits-all. Every account is configured per customer, from day one:
Your modules
Modules are switched on per account — start with the core platform and add CRM, Inventory, Store, or Training when you're ready. Changes apply immediately.
Your roles
Custom roles built from ~85 named permissions — an 'Auditor' or 'Store Supervisor' seat shaped to your org chart, not ours.
Your catalogs
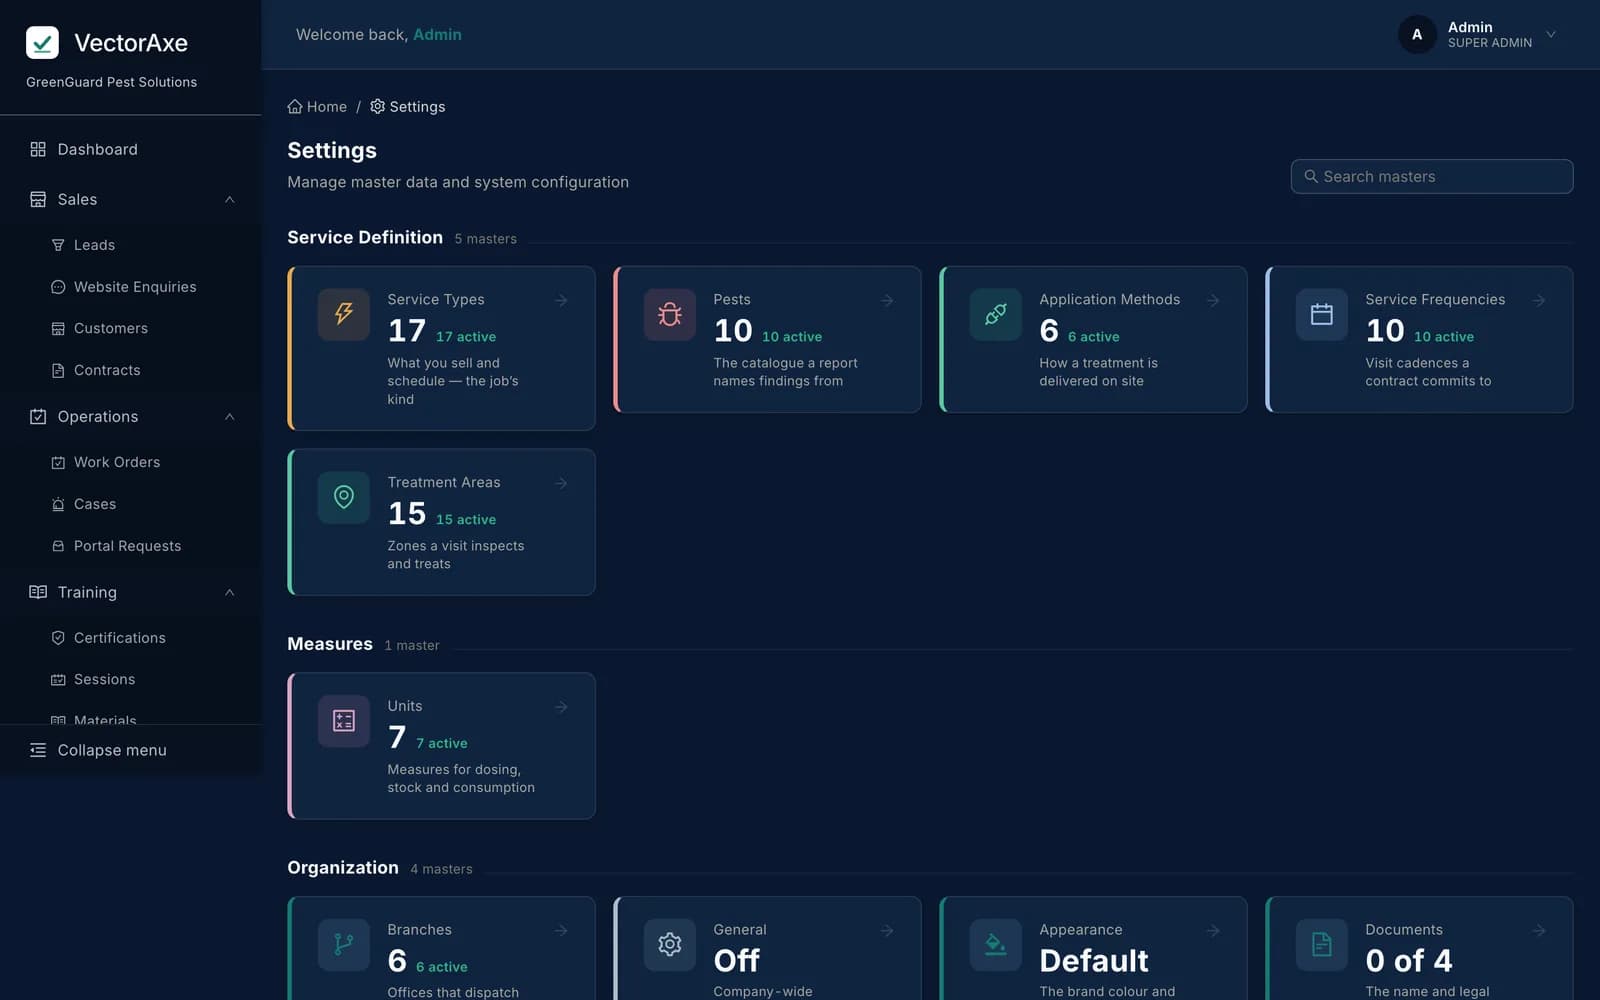
Service types, pests, treatment areas, and audit types are editable catalog data — matched to how you actually operate, not locked to our defaults.
Your brand
Your logo and color across your team's screens, your public website, your client portal, and every PDF you send.
For enterprise engagements we go further: module customization and tailored workflows, built with you — scoped and agreed as part of the engagement.
For enterprise brands
The brand's window: every vendor, every site, live.
How do you verify pest control happened at all 200 of your sites last month? When your vendors run on VectorAxe, your QA team gets a live portal per vendor — every visit, every audit observation, every report PDF, every invoice. Current, self-serve, and scoped to exactly the sites each user oversees.
The contract and audit workflows were shaped by real enterprise pest-control agreements — national food brands, QSR chains, e-commerce fulfilment centres — so the records your auditors need are captured by default, not reconstructed at review time.
Let's talk about your operation.
Multi-branch rollout, vendor programs, custom roles — bring your questions. We'll answer honestly, including about what's on the roadmap.
Your instincts. Our intelligence.